NIST-aligned risk assessments
We map every vulnerability to NIST, HIPAA, and GDPR controls, then hand you a prioritized action plan before a breach finds it first.
Most breaches start with a gap you can't see
A single overlooked misconfiguration often does the damage. Our assessment makes every vulnerability visible, so you can close the gap before attackers find it.
Ask us what every security check covers
Before you commit, know exactly what we examine. Here's the full scope of our risk assessment, so nothing slips through.
Network review
We map every device and connection on your network, looking for weak points attackers could use.
Access controls
We check who holds passwords and permissions, then flag accounts that should be locked down.
Policy check
We compare your security practices against NIST, HIPAA, and GDPR to find compliance gaps.
Threat scan
We test your systems for known vulnerabilities and suspicious activity before they become incidents.
Data review
We identify where your sensitive data lives and whether it's protected at rest and in transit.
Email security
We inspect your email setup for phishing risks and spoofing weaknesses that target your staff.
Backup audit
We verify your backup processes and recovery times so a breach doesn't become data loss.
Staff habits
We review common security behaviors and spot training gaps that put your systems at risk.
Wondering how the assessment actually works?
Our process is straightforward and practical. Each step builds on the last to deliver a clear action roadmap without disrupting your daily operations.
Initial discovery
We map your systems, data flows, and current security controls to understand your environment.
Vulnerability scanning
Automated tools and manual checks identify exposed ports, weak configurations, and outdated software.
Risk analysis
We assess likelihood and business impact for each finding, so you know what deserves immediate attention.
Compliance mapping
Findings are matched against NIST, HIPAA, and GDPR requirements to highlight regulatory gaps.
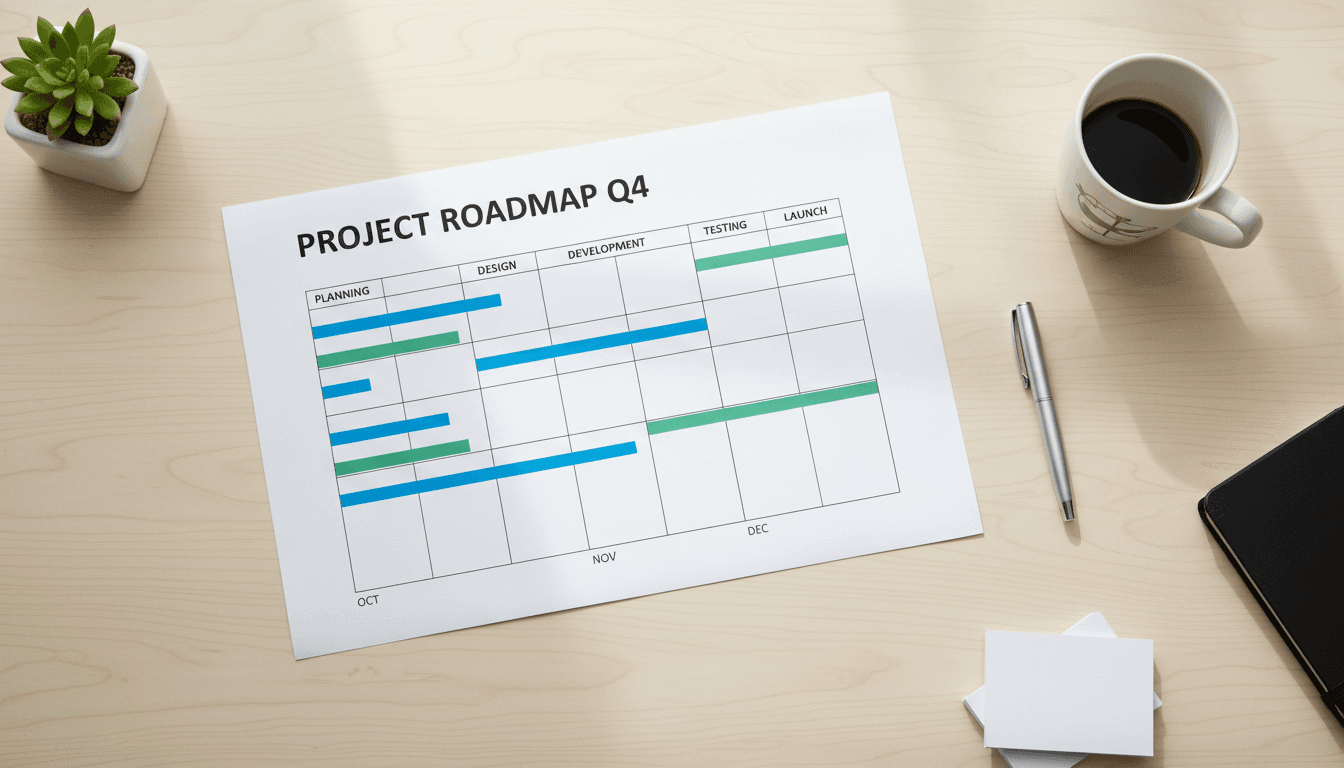
Action roadmap
You get a prioritized fix list with clear owners and timelines, plus guidance on immediate quick wins.
NIST-aligned reviews
Every gap gets mapped to controls you can act on.
Audit-ready findings
Delivered in language your auditors actually understand.
Most breaches happen to companies that think they're too small to matter
We work with growing businesses that have real data, real clients, and real compliance duties, but no dedicated security team to protect them.
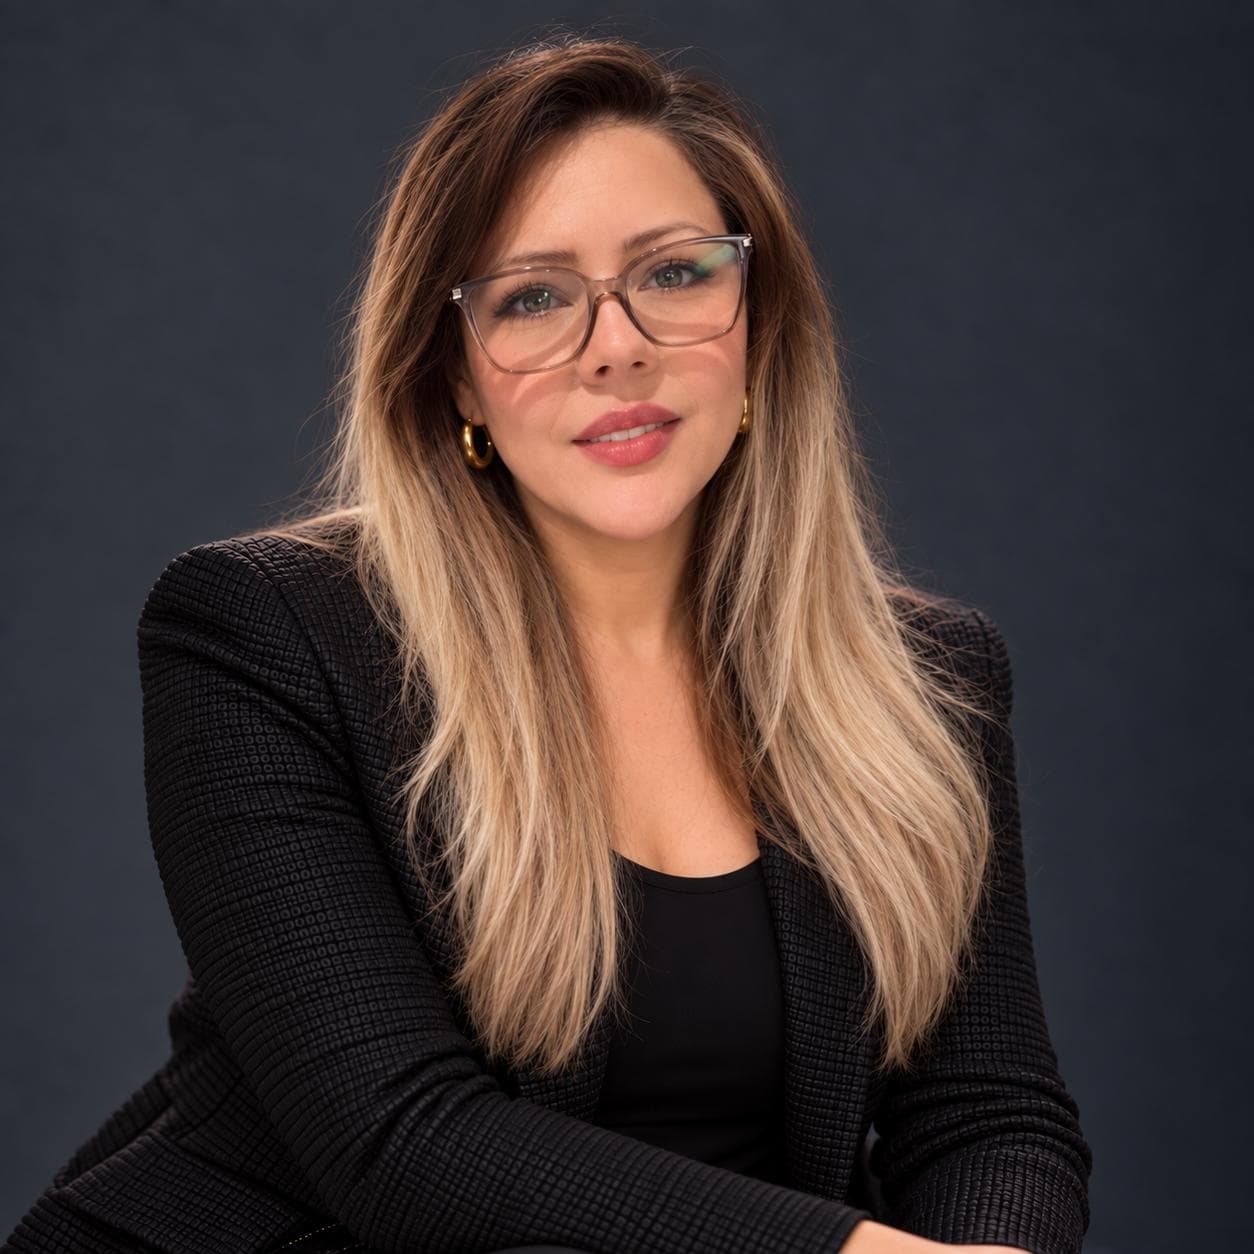
Security Lead & Co-Founder
Juliana Benavides
Juliana leads every assessment herself. She translates technical findings into plain language, so you know exactly what to fix and why it matters.

Risk Assessment Specialist
Marcus Reed
Marcus maps your environment against NIST, HIPAA, and GDPR controls. His reports flag the gaps that actually put your data at risk.
Your risk report, mapped to real fixes
Every assessment ends with a straightforward report you can act on, not a pile of technical noise.
3
Compliance frameworks
Findings mapped to NIST, HIPAA, and GDPR so you know exactly where you stand.
10+
Technical controls reviewed
From firewall rules to patch schedules, we test what attackers actually target.
30+
Pages of findings
A full written report with evidence, risk ratings, and context for every item.
90
Day action roadmap
Prioritized next steps ordered by risk so you can fix the serious gaps first.
Assessment answers
Straight answers on cost, timing, and what the assessment covers.
What does the risk assessment cost?
Pricing depends on your environment size and complexity. We scope it during a quick consultation, confirm the price before we start, and you never pay for work you didn't approve.
How long does the assessment take?
Most assessments wrap up within two to three weeks. Smaller environments can finish faster, and larger networks may need more time. We'll give you a clear timeline up front.
What standards do you check against?
We map every finding to NIST, HIPAA, and GDPR frameworks. That means you get a clear picture of where you stand and exactly what to fix for the regulations that apply to you.
Is this assessment just for large companies?
No. We run assessments for small teams, growing businesses, and established organizations alike. If you handle customer data, you have enough of a reason to understand your risk.
What do we receive when it's done?
You get a prioritized action roadmap that lists each vulnerability, the fix needed, and the order to tackle it in. No vague reports, just a clear path from risk to resolution.
What happens after we get the report?
We'll walk through the results with you and help you plan the next steps. Whether you work with us or handle fixes internally, the roadmap gives you a solid blueprint to follow.
Still have questions?
Ask us directly about cost, timing, or what's included in your assessment.
Schedule your 90-minute risk assessment
Get a clear picture of your exposure and a prioritized fix list, all before you make any decisions.